Cybersecurity analyst resume examples for fresher, mid-level & senior roles
Build an ATS-friendly Cybersecurity Analyst resume with complete role-specific examples, quantified bullet points, keyword guidance, and market advice for India, the US, and the UK.
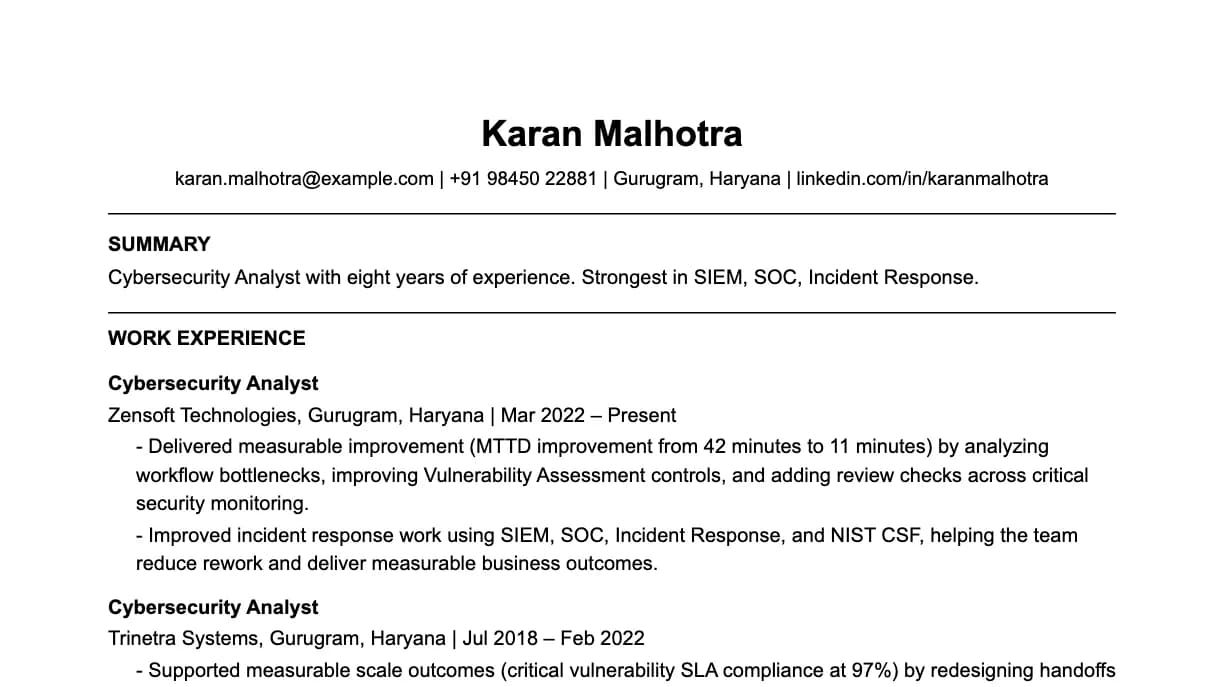
The bullets and skills are this page's own. The name, employer and dates are invented.
An applicant tracking system usually reads your resume as plain text before a person does. This page covers what that text should hold for cybersecurity analyst roles: the words postings use, bullets with real numbers in them, and a layout a parser can read. Every example here is invented, written to show how specific a strong cybersecurity analyst resume gets.
Must-have skills for a cybersecurity analyst resume
These skills come up often in cybersecurity analyst job postings, and recruiters search their ATS for them. Include every one you genuinely have, in the words the posting uses.
Pro tip: mirror the job description exactly
If the job description says "React.js" and you write "React", a recruiter searching for the exact term may not find you. Use the posting's phrasing and acronyms in your skills section and bullet points, where they are true of you.
Strong cybersecurity analyst resume bullet examples
Every bullet below follows the same formula: strong action verb + what you did + quantified impact. Study the structure, then replace the numbers with your real achievements. Generic bullets like "responsible for X" tell a recruiter nothing about what you achieved.
Action
Start with Built, Reduced, Migrated, Designed, Optimized, Led.
Tools
Name the exact tool or method: SIEM, SOC, Incident Response, NIST CSF.
Impact
End with a number: time saved, cost, volume, quality, or people served.
Cybersecurity Analyst - Performance
01
Delivered measurable improvement (MTTD improvement from 42 minutes to 11 minutes) by analyzing workflow bottlenecks, improving Vulnerability Assessment controls, and adding review checks across critical security monitoring.
Cybersecurity Analyst - Product Delivery
02
Improved incident response work using SIEM, SOC, Incident Response, and NIST CSF, helping the team reduce rework and deliver measurable business outcomes.
Cybersecurity Analyst - Scale
03
Supported measurable scale outcomes (critical vulnerability SLA compliance at 97%) by redesigning handoffs between SIEM, SOC, and Incident Response while improving visibility, ownership, and follow-through.
Cybersecurity Analyst - Automation
04
Delivered measurable efficiency gains (a 36% reduction in repeat phishing incidents) by replacing manual steps with repeatable SIEM workflows, documented SOPs, and quality checks used by cross-functional teams.
Entry-Level Cybersecurity Analyst - Projects
05
Built a portfolio-ready security monitoring project with SIEM, SOC, Incident Response, NIST CSF, and OWASP Top 10, sample reports, documented process notes, and measurable before-after results.
Senior Cybersecurity Analyst - Leadership
06
Mentored 5 team members on SIEM, SOC, and Incident Response standards and introduced review templates that improved delivery consistency across quarterly goals.
Common mistake: weak action verbs
Avoid passive openers like "Responsible for", "Helped with", or "Worked on". These tell the recruiter nothing about your actual contribution. Replace them with ownership verbs: Built, Designed, Led, Reduced, Launched, Architected, Negotiated, Delivered. Then always end with a number.
The bullets above, in a finished resume
Rendered by the same exporter the builder uses, in an ATS-safe single-column template. No tables and no side columns, because that is what the format advice further down this page tells you to avoid.
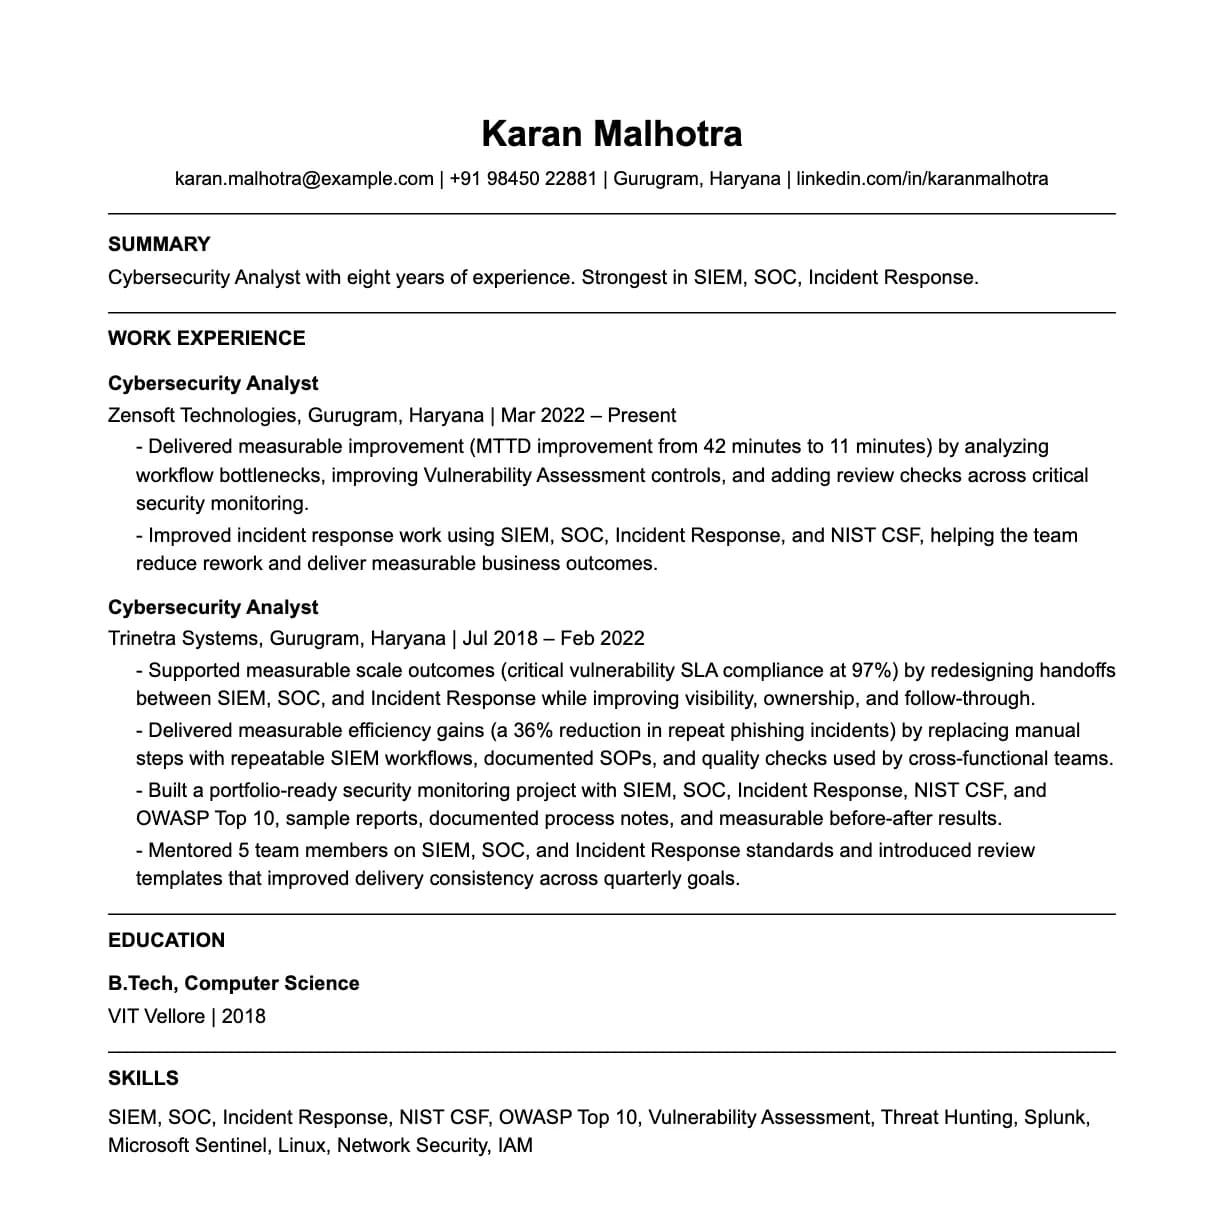
The bullets and skills are this page's own. The name, employer and dates are invented.
Complete cybersecurity analyst resume examples
These are fictional examples in a single-column layout that ATS parsers read cleanly. Use the structure, keyword placement, and achievement density as a model; replace names, companies, and metrics with your own verified details.
Entry-level cybersecurity analyst resume example
Vivek Pandey
SOC Analyst L1 | Splunk alert triage, phishing analysis, incident response
Pune, India | vivek.pandey@example.com | +91 90000 14085
linkedin.com/in/vivek-pandey-soc | github.com/vivekpandey-sec
Professional Summary
SOC analyst with 1 year of 24x7 monitoring at a managed security provider. Triages SIEM alerts in Splunk, investigates phishing reports, escalates incidents with clear notes and writes small Python and Bash scripts to speed up routine checks.
Skills
Security: SIEM (Splunk/Microsoft Sentinel), Incident Response, Phishing analysis, Network Security, Threat Intelligence
Tools: Splunk, Wireshark, Nessus, VirusTotal, Linux
Scripting: Python/Bash Scripting
Experience
SOC Analyst L1 | Trinetra Cyber Defence Pvt Ltd
Pune, India | Jul 2025 - Present
• Triage about 120 SIEM alerts a shift in Splunk for 9 client companies, escalating confirmed incidents to L2 within the 15-minute target.
• Analysed 400+ reported phishing emails, blocked malicious domains and wrote 6 detection rules from repeated patterns.
• Wrote a Python script that enriches alerts with threat intelligence lookups, saving about 3 minutes per alert.
• Drafted 2 incident response runbooks for brute-force and suspicious PowerShell alerts, now used by the whole L1 team.
Projects
Home SOC lab | Wazuh, Wireshark, Kali Linux, VirtualBox
• Built a small lab with a Windows and a Linux host, simulated attacks and wrote detection rules and write-ups for each.
Education
B.Tech in Computer Engineering, Savitribai Phule Pune University - 2025
Certifications
CompTIA Security+
Why this resume works
• Bullets use the language of SOC work (triage, escalation, detection rules) with real volumes.
• The home lab shows curiosity and hands-on practice, which matters for entry-level security roles.
• One relevant certification is listed instead of a long list of short courses.
Mid-level cybersecurity analyst resume example
Nandini Reddy
Cybersecurity Analyst | Microsoft Sentinel, CrowdStrike, vulnerability management
Hyderabad, India | nandini.reddy@example.com | +91 90000 14092
linkedin.com/in/nandini-reddy-security
Professional Summary
Security analyst with 5 years in SOC and vulnerability management for a fintech and a large IT services firm. Leads investigations in Microsoft Sentinel and CrowdStrike, runs the monthly Nessus scan and patch cycle, and supports ISO 27001 audits.
Skills
Security operations: SIEM (Splunk/Microsoft Sentinel), Incident Response, Threat Intelligence, CrowdStrike, Firewall Management
Vulnerability management: Nessus, Vulnerability Management, Penetration Testing support, Patch tracking
Governance: ISO 27001, NIST Framework, Cloud Security
Experience
Cybersecurity Analyst | Krishna Fintech Services Pvt Ltd
Hyderabad, India | May 2023 - Present
• Lead investigations for medium and high severity incidents in Microsoft Sentinel and CrowdStrike, with mean time to contain down from 5 hours to 90 minutes.
• Run monthly Nessus scans across 1,400 assets and track fixes with IT; critical findings older than 30 days fell from 85 to 6.
• Prepared evidence for the ISO 27001 surveillance audit with no major non-conformities.
• Reviewed firewall rules with the network team and removed 300+ unused or overly broad rules.
SOC Analyst | Bhagyanagar IT Services Ltd
Hyderabad, India | Jul 2021 - Apr 2023
• Monitored Splunk alerts for 3 enterprise clients and moved from L1 to L2 within a year.
• Tuned 25 noisy detection rules, cutting false positives by about 40%.
Education
B.Tech in Computer Science and Engineering, JNTU Hyderabad - 2021
Certifications
Certified Ethical Hacker (CEH), EC-Council | Microsoft Certified: Security Operations Analyst Associate (SC-200)
Why this resume works
• The headline names the exact tools most mid-level SOC job posts ask for.
• Results use security measures (time to contain, aged critical findings) instead of vague claims.
• Audit and firewall work show she can work beyond alert triage.
Senior cybersecurity analyst resume example
Harpreet Singh Gill
Senior Security Analyst | Security operations lead, zero trust, cloud security, NIST
Mohali, India | harpreet.gill@example.com | +91 90000 14099
linkedin.com/in/harpreet-singh-gill-security
Professional Summary
Security professional with 12 years in banking and IT services, the last 5 leading security operations for a mid-sized lender. Runs a team of 7 analysts, owns the incident response plan, and drove a zero trust and cloud security programme mapped to the NIST Framework and RBI guidelines.
Skills
Leadership: Security operations, Incident Response, Risk Assessment, Team building
Technical: SIEM (Splunk/Microsoft Sentinel), CrowdStrike, Zero Trust, Cloud Security, Network Security, Penetration Testing
Frameworks: NIST Framework, ISO 27001, RBI cyber security guidelines
Experience
Senior Security Analyst, SOC Lead | Satluj Finance Ltd
Mohali, India | Jun 2021 - Present
• Lead a 7-person SOC covering 6,000 endpoints and 220 branches, with 24x7 coverage shared with a managed partner.
• Rolled out a zero trust access model with MFA and device checks for all remote and vendor access, ending shared VPN accounts.
• Rewrote the incident response plan and ran 4 tabletop exercises a year with IT, legal and leadership.
• Planned the annual penetration testing programme and closed 95% of high findings within the agreed 45 days.
Information Security Analyst | Shivalik Technology Services Pvt Ltd
Chandigarh, India | Jul 2016 - May 2021
• Managed SIEM content and threat hunting for 5 banking clients.
• Led cloud security reviews for 12 client workloads moving to public cloud.
Network Security Engineer | Punjab Netlink Pvt Ltd
Ludhiana, India | Jul 2014 - Jun 2016
• Managed firewalls and VPNs for 40 enterprise customers.
Education
B.E. in Electronics and Communication Engineering, Panjab University, Chandigarh - 2014
Certifications
CISSP, ISC2 | Certified Information Security Manager (CISM), ISACA
Why this resume works
• The summary gives scale and leadership scope up front, which is what senior security roles screen for.
• Bullets show programme-level work (zero trust, IR plan, pentest cycle) rather than single alerts.
• Earlier roles show a believable path from network security to SOC leadership.
Cybersecurity analyst ATS keyword matrix
Recruiters search their ATS for the terms in the posting. Use this matrix to decide which cybersecurity analystkeywords belong in your skills section, work bullets, project descriptions, and summary.
Role Title Match
High
Use the closest target title in the headline, summary, and most recent experience title when accurate.
Core Stack
High
Skills section, project stack lines, and first two experience bullets.
Execution Keywords
Medium
Experience bullets that show how the work was built, tested, shipped, or measured.
Business Impact
High
End each major bullet with a metric or observable outcome.
Weak vs strong cybersecurity analyst resume bullets
This is the fastest way to improve the page quality and the resume quality: turn vague responsibility statements into measurable engineering outcomes.
Weak bullet
01
Worked on security monitoring using SIEM.
Strong bullet
Delivered measurable improvement (MTTD improvement from 42 minutes to 11 minutes) by applying SIEM, SOC, Incident Response, and NIST CSF to a high-impact security monitoring workflow.
The stronger version gives scope, tools, and a measurable result.
Weak bullet
02
Responsible for fixing bugs and supporting releases.
Strong bullet
Reduced recurring quality issues by adding SOP checks, clearer acceptance criteria, and ownership notes for incident response workflows.
It reframes responsibility as ownership and measurable quality improvement.
Weak bullet
03
Made dashboards and reports for the team.
Strong bullet
Built stakeholder-ready reporting that highlighted a 36% reduction in repeat phishing incidents and helped prioritize the next cycle's decisions.
It shows why the work mattered, not only what was produced.
Weak bullet
04
Good communication and teamwork skills.
Strong bullet
Coordinated with product, design, QA, and operations to ship risk reduction improvements with documented decisions and fewer handoff delays.
Soft skills become credible when tied to a real delivery context.
Cybersecurity analyst resume writing guide
Three areas where most cybersecurity analyst resumes either win or lose against the competition. Read each section carefully, even one improvement here can meaningfully increase your response rate.
What the best cybersecurity analyst resumes show
The strongest cybersecurity analyst resumes do not list tools in isolation. They connect SIEM, SOC, Incident Response, NIST CSF, OWASP Top 10, Vulnerability Assessment, Threat Hunting, and Splunk to real work, measurable outcomes, and the hiring team's exact target role. Use the examples on this page as model resumes, then adapt the metrics to your real projects.
Cybersecurity analyst resume format for ATS
Use a clean reverse-chronological format with standard headings: Summary, Skills, Experience, Projects, Education, and Certifications. Put core keywords such as SIEM, SOC, Incident Response, NIST CSF, OWASP Top 10, Vulnerability Assessment, Threat Hunting, and Splunk in both the skills section and the work bullets so ATS systems and human reviewers see context.
How to market this cybersecurity analyst resume
For job boards, LinkedIn, and referrals, mirror the job description's role title when accurate, then customize the top six skills and first three bullets. For AI answer engines, clear questions and answers help the page surface for searches like "best cybersecurity analyst resume example", "ATS keywords for cybersecurity analyst", and "cybersecurity analyst resume for freshers".
Cybersecurity analyst salary in India
Self-reported ranges for the Indian market. Actual pay varies by city, company size and negotiation; metros typically sit above these bands.
Entry Level (0–2 yrs)
₹4 – 8 L/yr
India CTC estimate, FY 2025–26
Mid Level (3–6 yrs)
₹10 – 22 L/yr
India CTC estimate, FY 2025–26
Senior Level (7+ yrs)
₹25 – 55 L/yr
India CTC estimate, FY 2025–26
Self-reported salary data for India, approximate CTC per year. Verify against AmbitionBox.
How to use these numbers
They are national and cross-industry, so your city and sector move them a long way. Use the median as the anchor, name a specific number rather than a range, and justify it with the single most quantified achievement on your resume.
Cybersecurity analyst resume format and structure
Standard section names in a familiar order are easiest for an ATS to parse and for a recruiter to skim. Use this structure:
Section 01
Contact information
Name, professional email, phone, LinkedIn URL, and city/country. No photo, no date of birth, no full address. Keep it to 2 lines maximum.
Section 02
Professional summary
2-3 sentences. Years of experience as a cybersecurity analyst, your primary specialty, and your single biggest quantified achievement. No fluff.
Section 03
Work experience
Reverse-chronological order. Company name, your title, dates (month/year), location. 3–5 bullet points per role, each with a number. Most recent role gets the most bullets.
Section 04
Skills
List SIEM, SOC, Incident Response, NIST CSF, OWASP Top 10, and other relevant tools. Group by category if you have 10+ skills.
Section 05
Education
Degree, institution, graduation year. No GPA unless above 3.5 and within 3 years of graduation. Certifications go here or in a separate Certifications section.
Section 06
Optional sections
Projects (essential for early-career), Certifications, Publications, Open Source, or Languages. Only include if genuinely adding signal.
Cybersecurity analyst resume guidance by market
The same cybersecurity analyst resume should not read exactly the same in every market. These are the adjustments that matter to recruiters in each.
United States
• Use a one-page resume for early career candidates and keep bullets outcome-led.
• Tie SIEM, SOC, Incident Response, and NIST CSF to business metrics, production reliability, customer experience, or engineering efficiency.
• Avoid photos, marital status, date of birth, or full address.
UK / Europe
• Use a CV-style format only when the employer expects it; otherwise keep the structure concise and achievement-led.
• Include work authorization only when relevant and helpful.
• Use plain section labels so ATS systems can parse skills, experience, education, and certifications cleanly.
India
• Lead with Cybersecurity Analyst in the title and show hands-on proof through internships, projects, or production systems.
• For fresher resumes, add GitHub links, project metrics, and tools used. Avoid long objective statements.
• Mention notice period, location preference, and cloud or certification details only when they strengthen the target role.
Questions
Cybersecurity analyst resume, frequently asked questions
Answers to the most common questions job seekers have when writing a cybersecurity analyst resume, covering format, keywords, length, and ATS optimization.
Resume examples for other roles
Need a guide for a different job title? Each page includes role-specific ATS keywords, real bullet examples, and a writing guide.
Build your cybersecurity analyst resume
Use our free tools to build, score, and optimize your resume for the specific job description you're applying to.
Sources and references
Where the skills, tooling and pay figures on this page come from.
From example to yours
Start from this, then make it yours
The builder takes an example like this one and lets you edit it in place. The score updates as you type, so you can see whether a change helped rather than guessing.
Open the builder
The real resume library, on a sample account with sample scores.
Build your cybersecurity analyst resume, free
Start from an example like this in the builder and watch the score move as you edit. Building, scoring and a watermarked export are free, with no card.